Build Fast. Stay in Control.

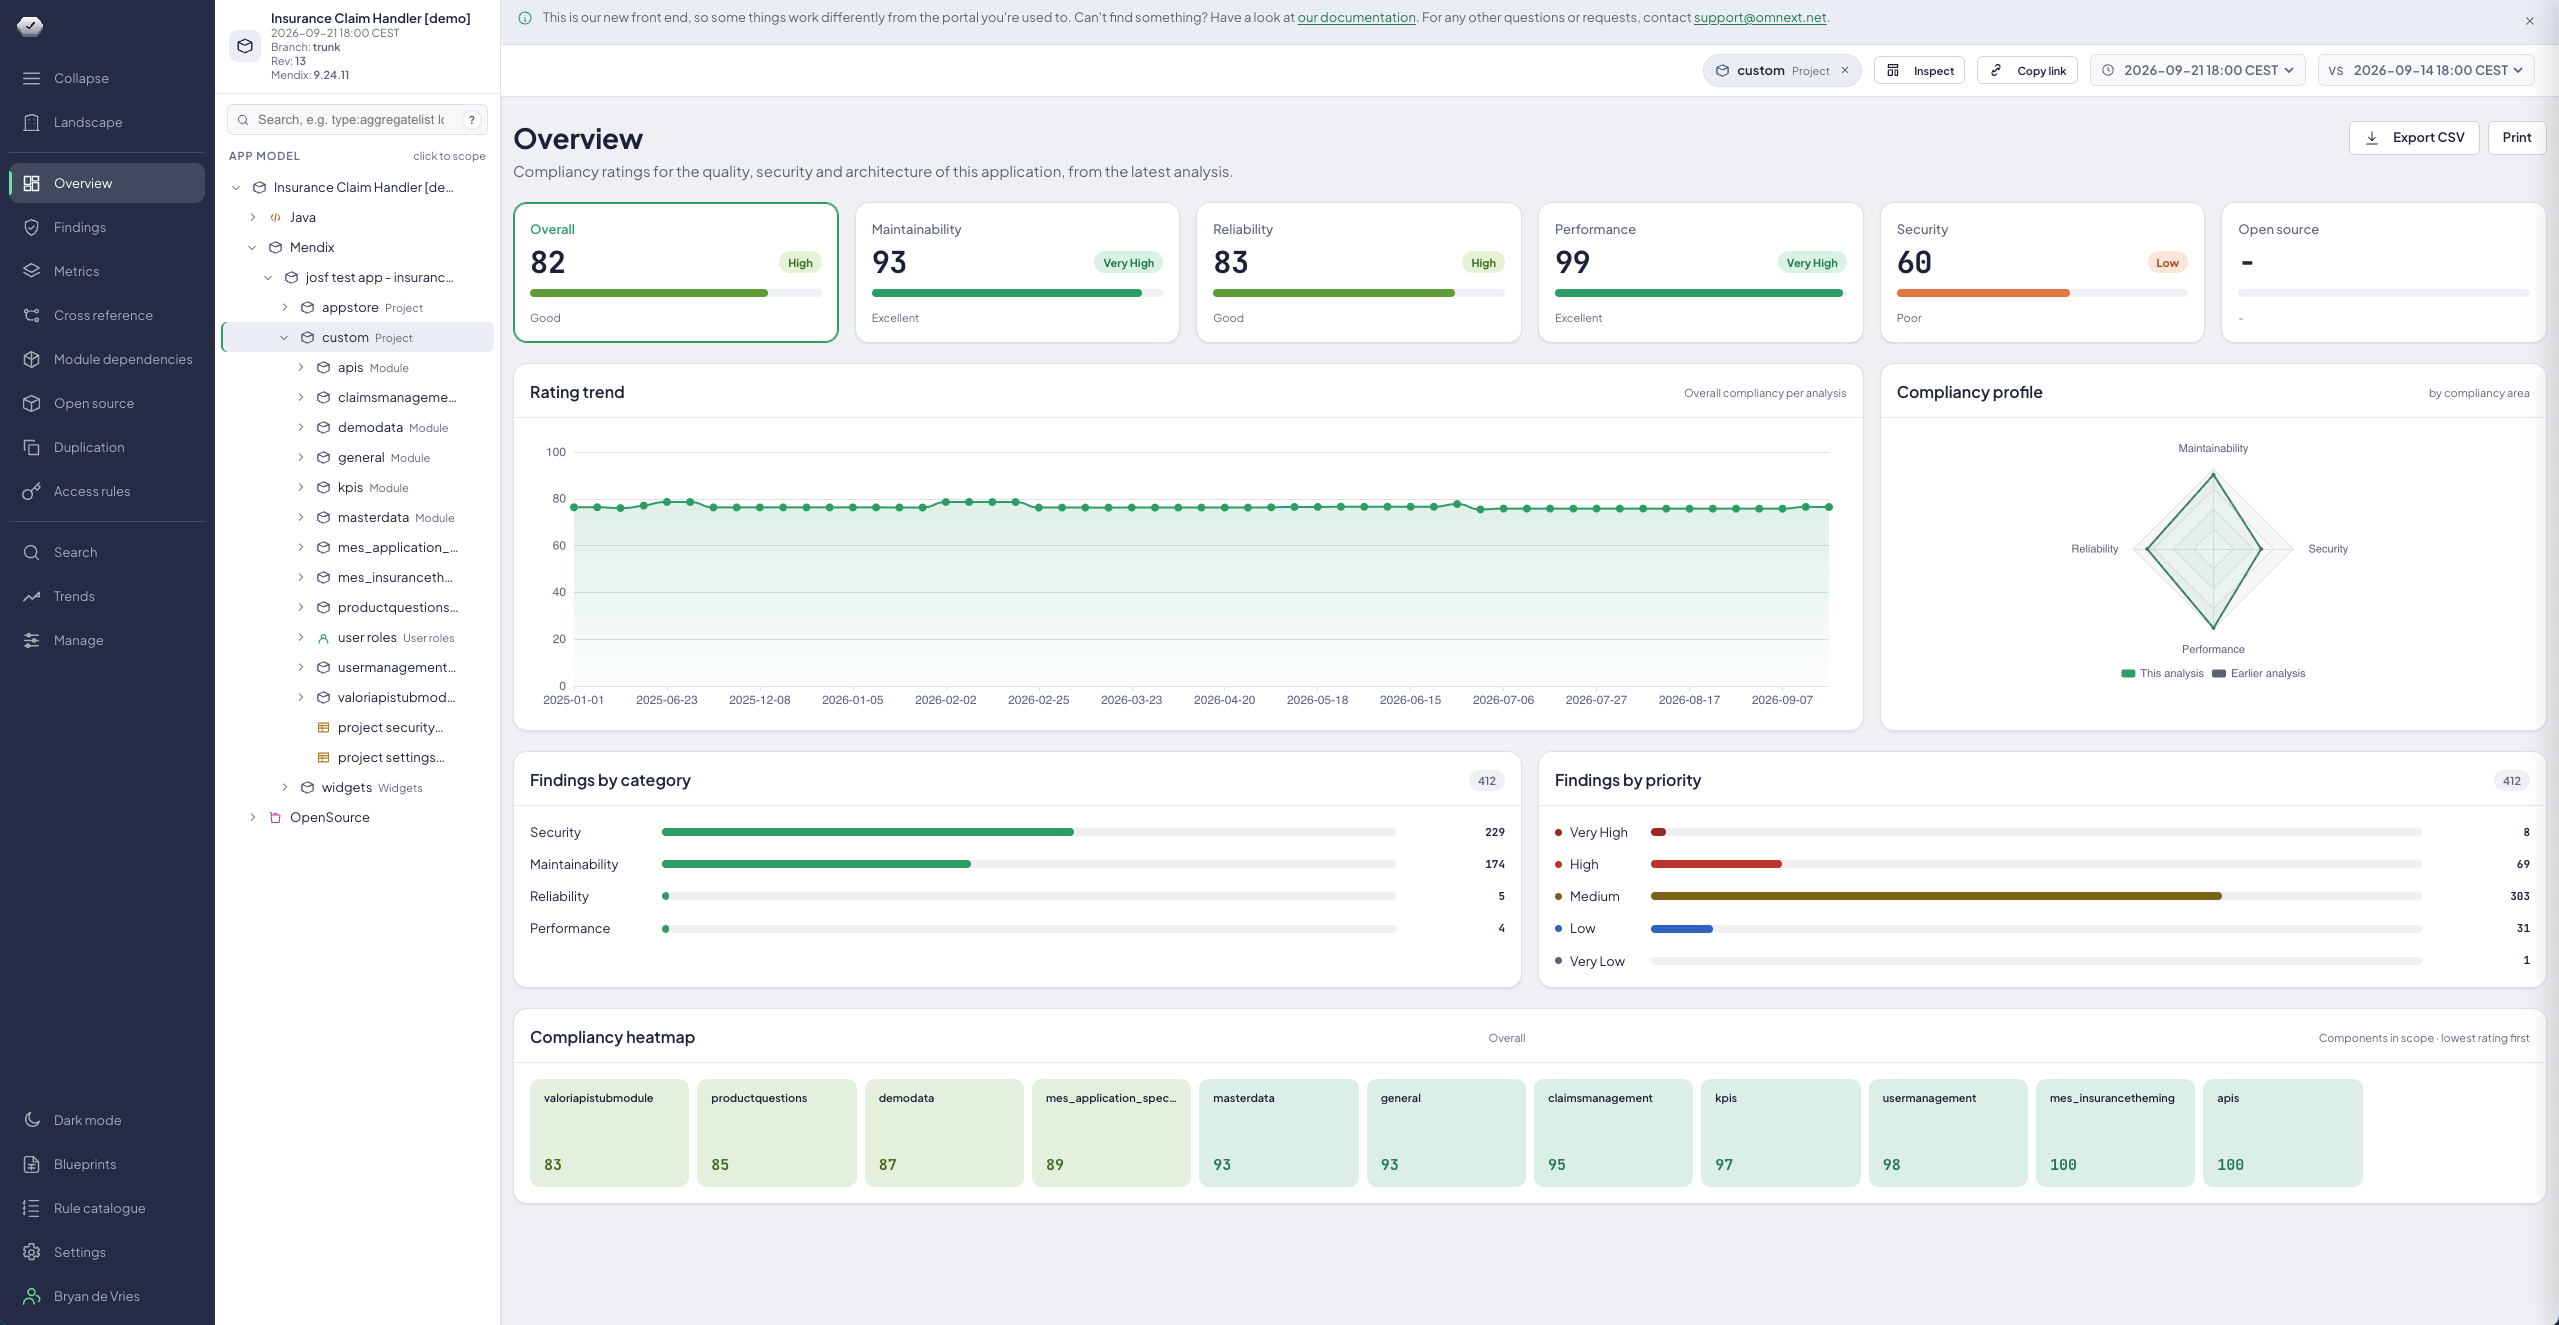
Low-code speed quietly erodes maintainability, performance and reliability. Inter-module dependencies and architecture drift pile up as technical debt while teams keep shipping. A CoE cannot peer-review 100 apps by hand.
Set the priorities and thresholds that matter to you. Toggle rules on or off; Omnext curates the live ruleset.
See exactly what causes each dependency and where the architecture drifts.
Java actions checked against Java best practices and ISO 25010.
Portfolio and application level, with progress reporting over time.
Analyses run with every change through the Omnext API.
The same scan inside Studio Pro, and results your AI assistants can consult.
Read moreThe Omnext Compliancy Rating is absolute, formula-based and reproducible. Not a benchmark: the same model scores the same twice, and every drop traces to a specific rule, area and penalty. Risk classification runs from below 50 (very high) through 50 to 70 (high), 70 to 85 (medium), 85 to 95 (low) and 95 to 100 (very low).
Complexity, duplication, size and structure of microflows, pages and modules.
Patterns that slow the app down at runtime: retrieves, loops, indexes.
Error handling, validation and consistency of the model.
Fed by the Security Analysis module along the S-Unit Top 10.
Give Omnext access to the Mendix model. Nothing is installed, nothing touches production.
Results on the dashboard within hours. Onboarding, training and SSO configuration are free.
Per sprint, daily or in the pipeline. Findings, trends and audit trail in one place.
A demo takes an hour. Unlimited scans and users are included.