Security Analysis · SAST for Mendix
Security Analysis for Mendix
Build Fast. Stay Secure. Built with The S-Unit, the Mendix security specialists.
Access rule analysis
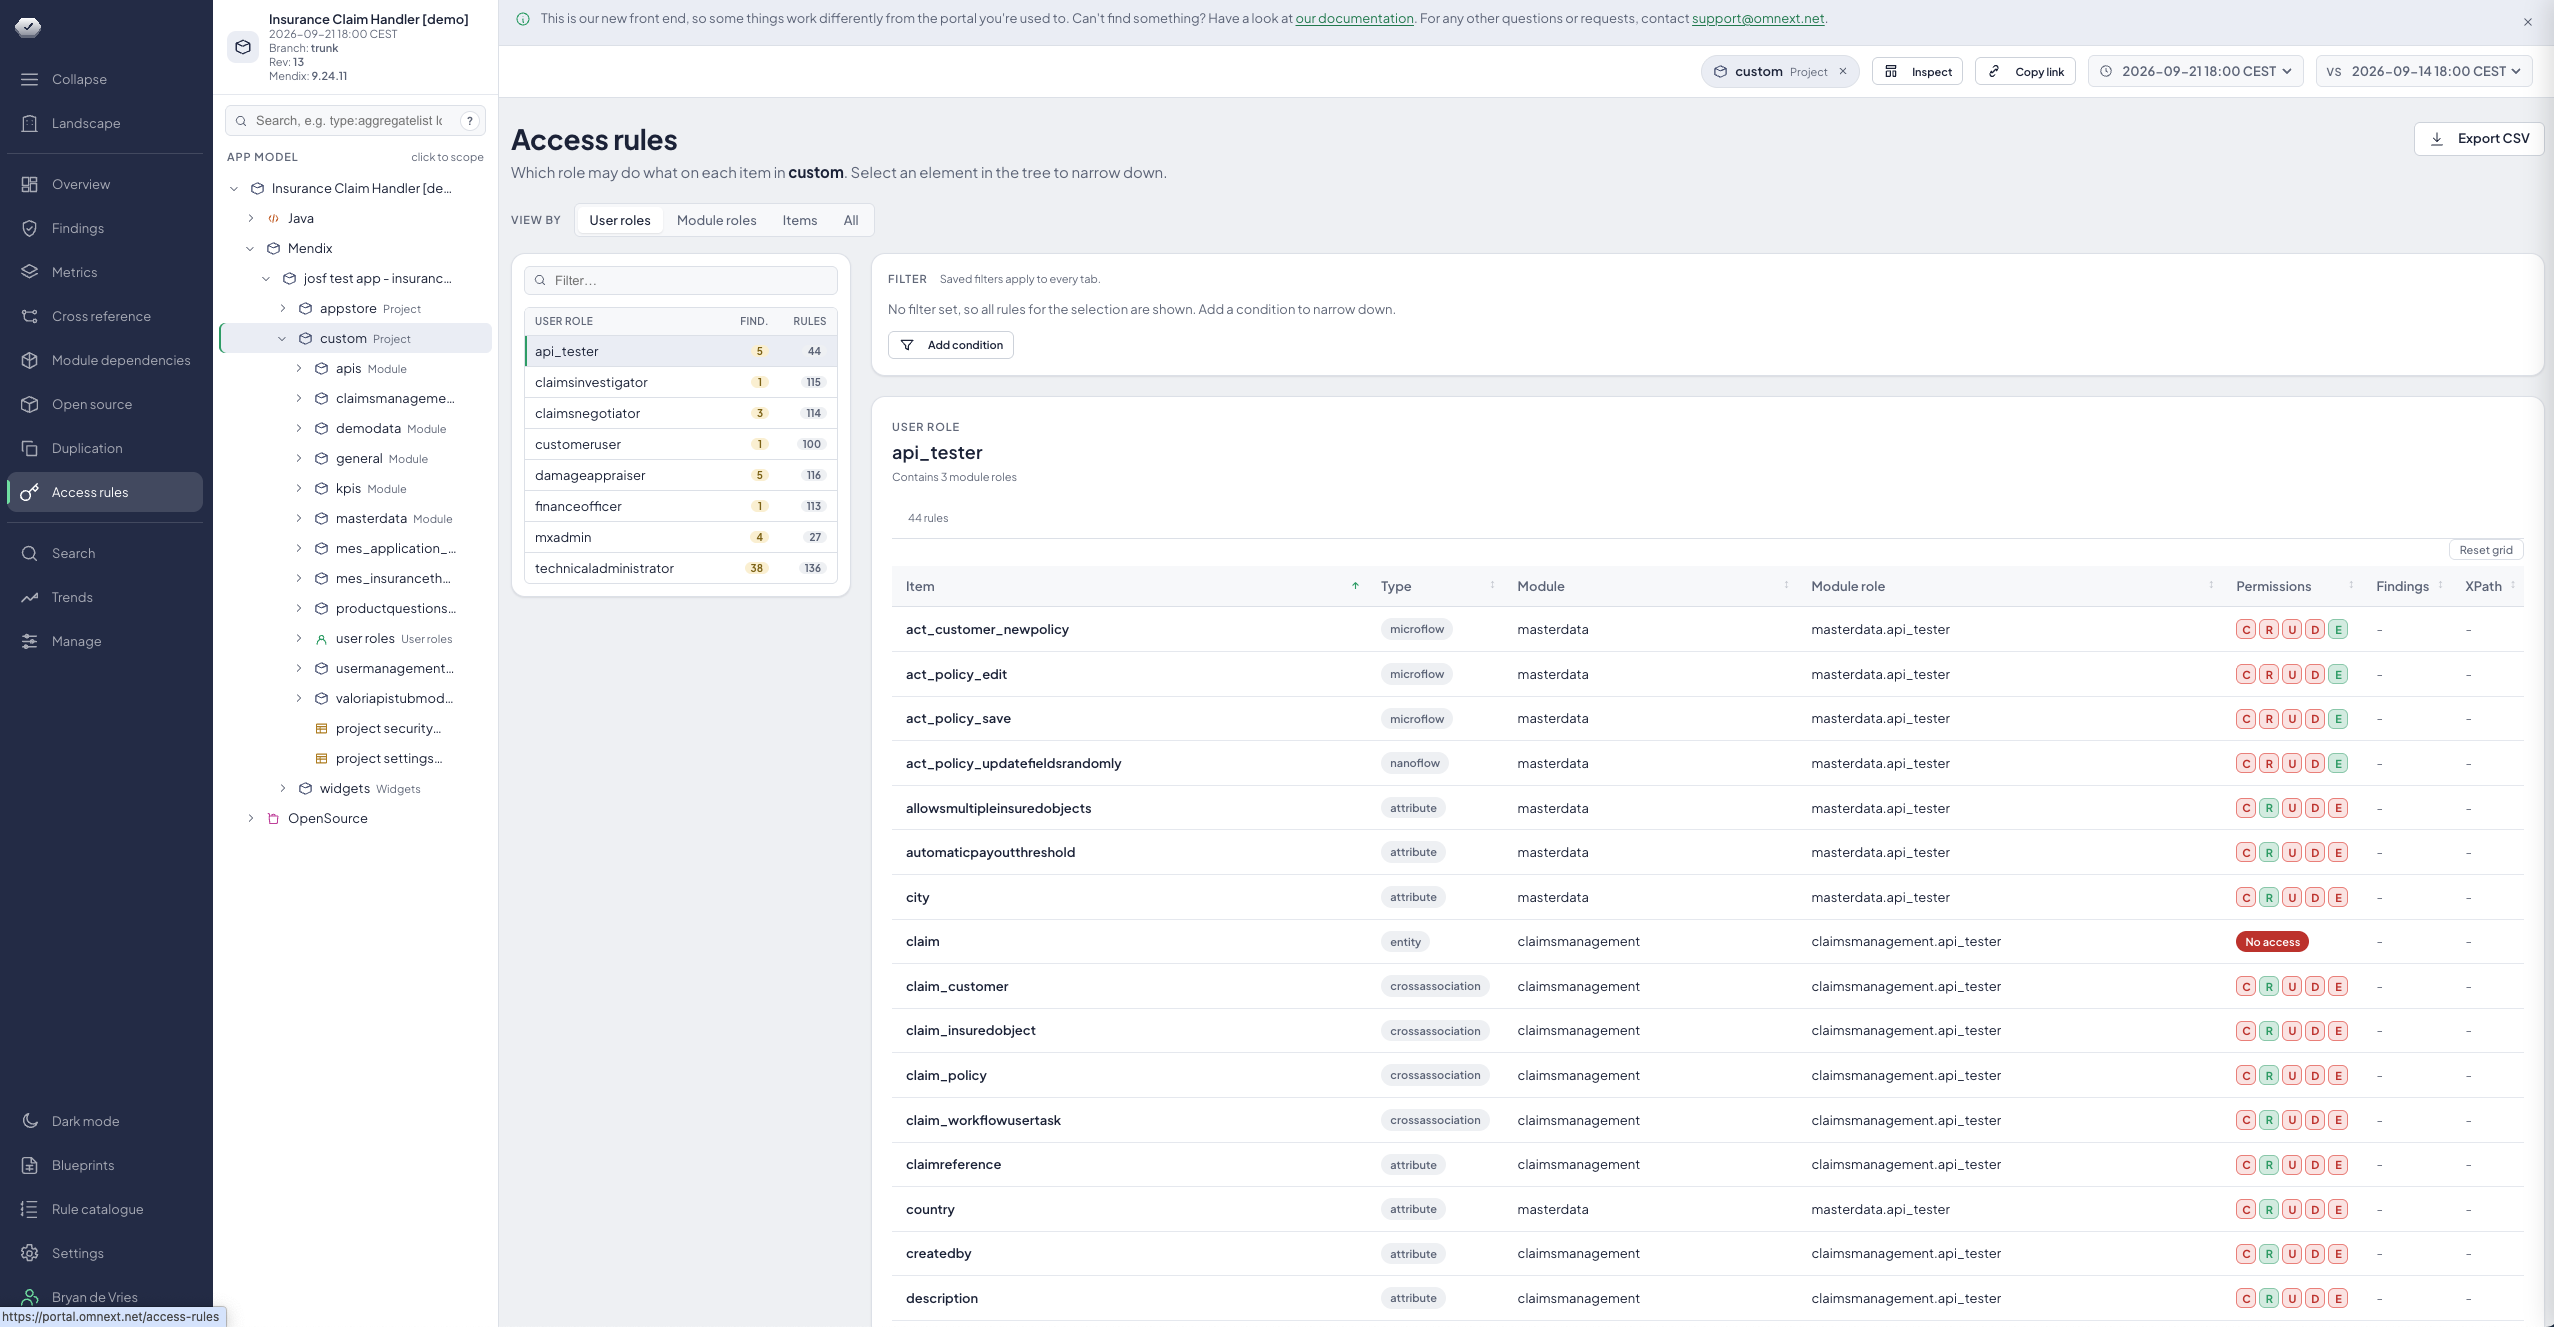
Who can Create, Read, Update, Delete or Execute what?
The CRUDE matrix shows every user role against every entity, microflow and nanoflow. Misconfigured access rules are the classic cause of data exposure in Mendix apps.
Full CRUDE matrix per module role and user role
Anonymous access and XPath constraints checked
Audit-ready export for compliance reviews
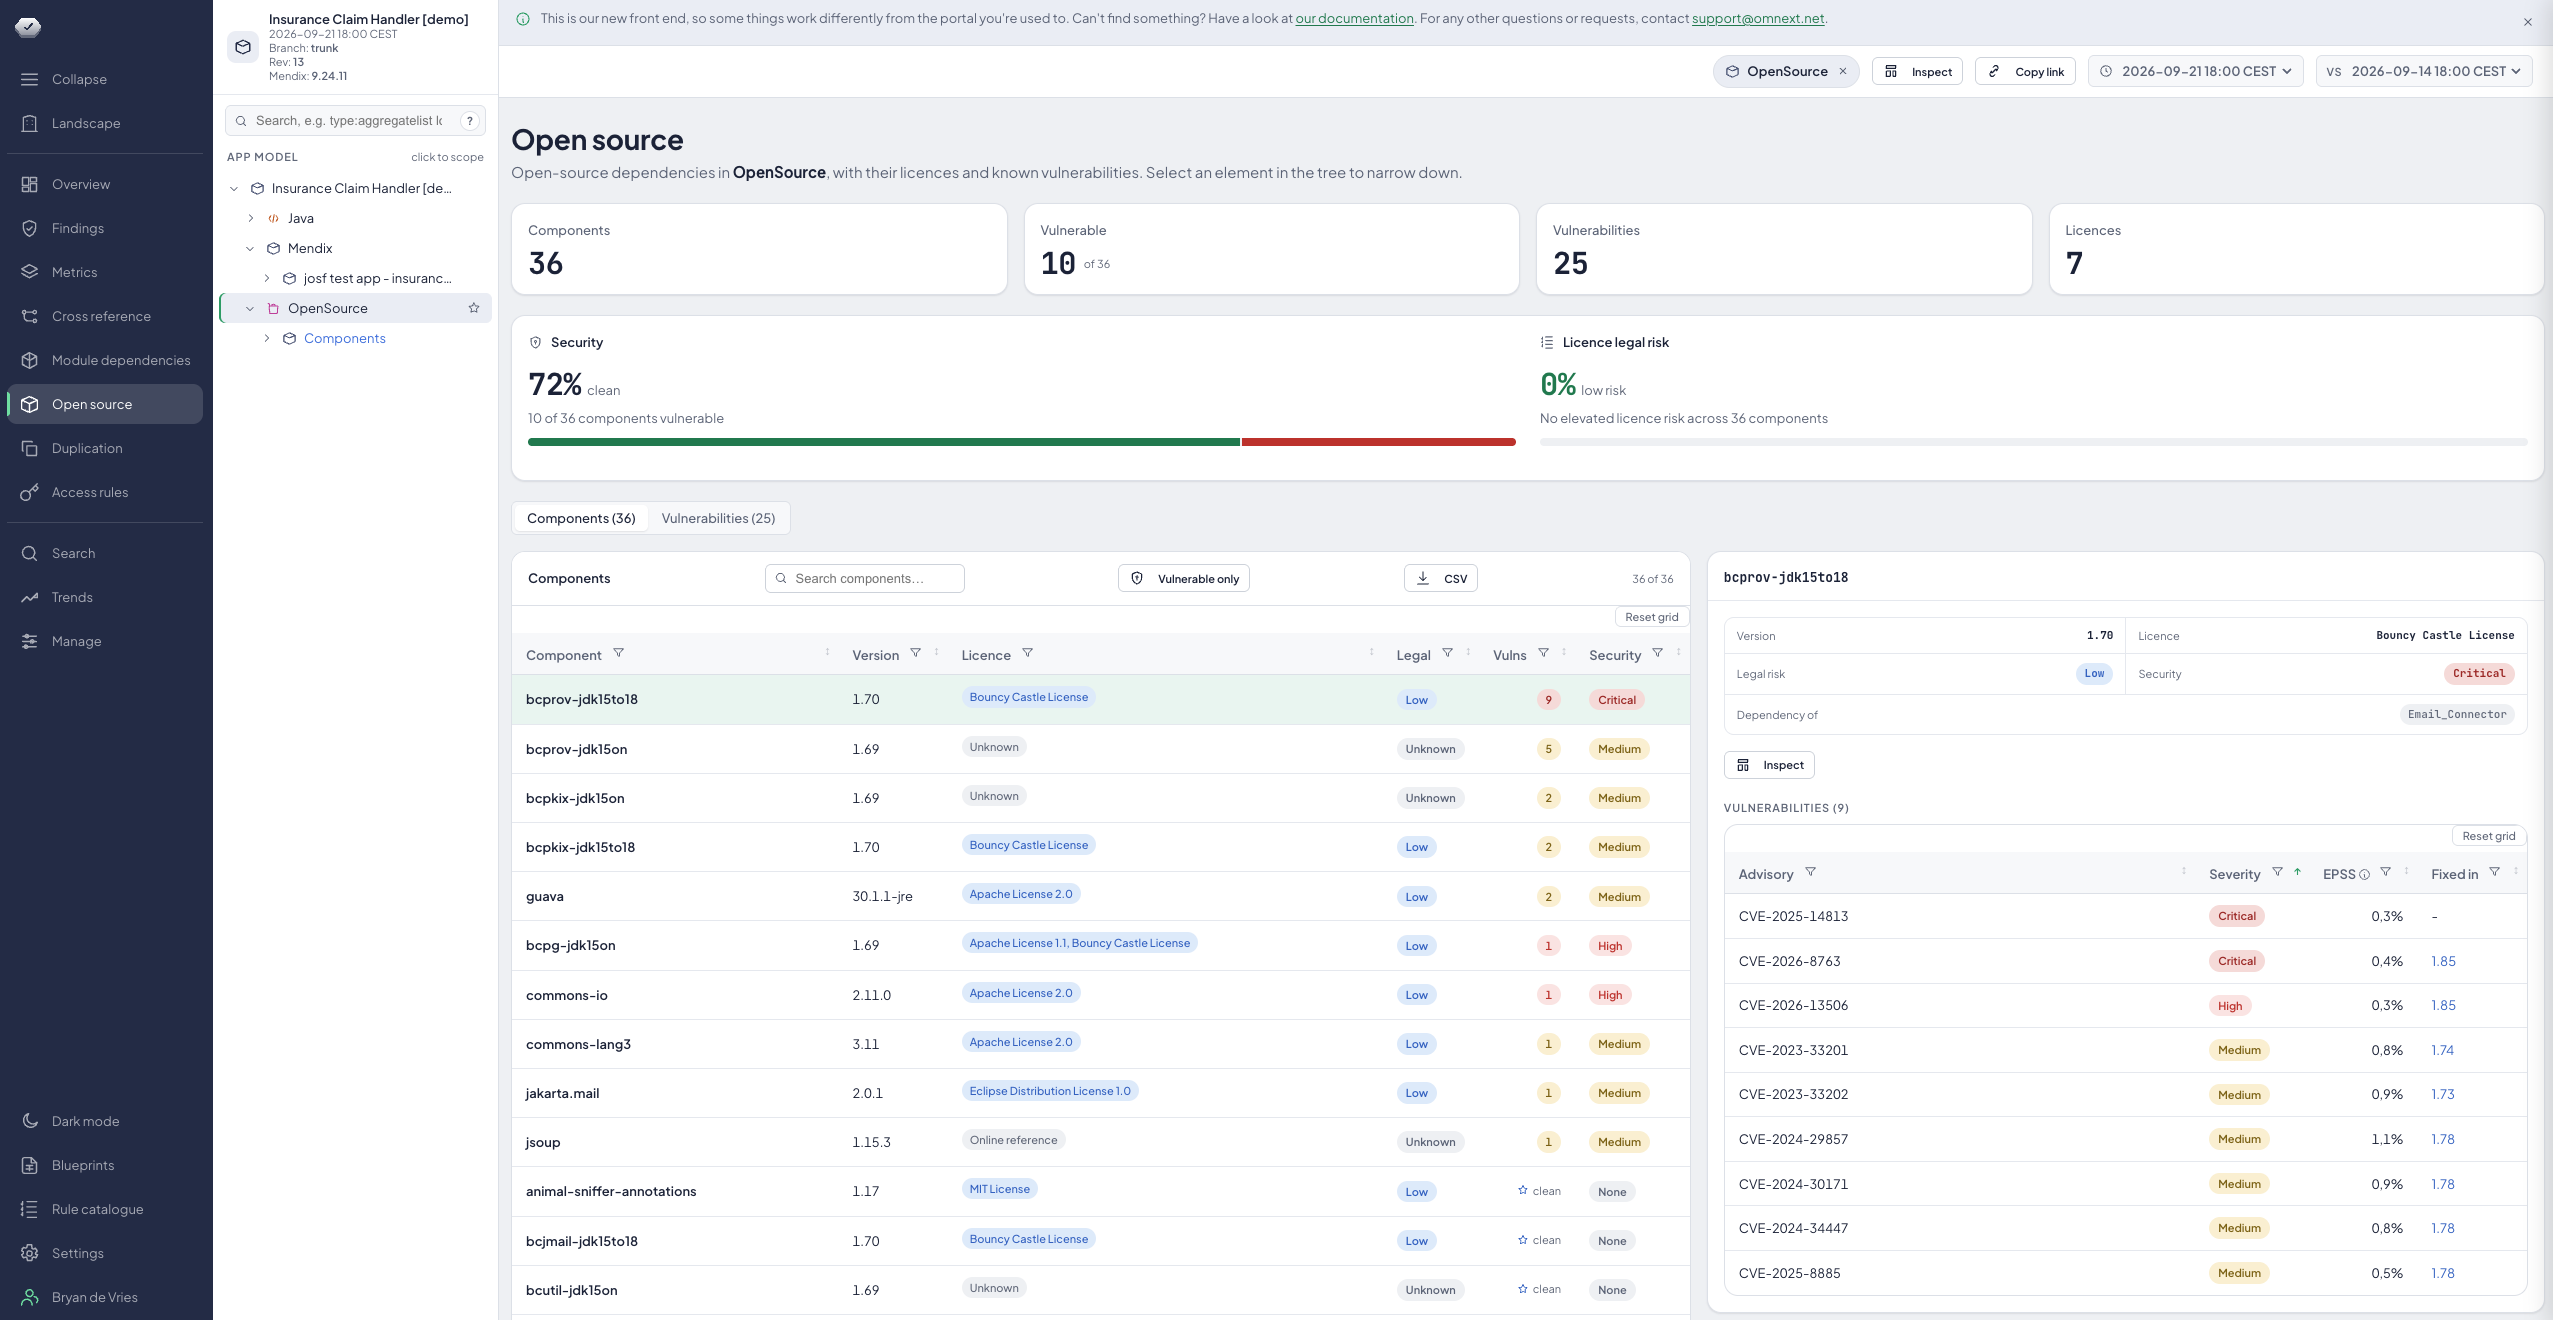
Open source & SBOM
Half of your application is somebody else's.
Marketplace modules, widgets, JAR and JavaScript components: Omnext builds the SBOM, flags risky licences and matches known CVEs via NIST.
SBOM per application and per portfolio
Licence risk such as GPL and IP exposure
CVE prevalence and exploit probability per component