Software Quality & Security for Mendix
Simplified quality governance.
Superior insights and control.

Automated quality and security analysis for Mendix, from Studio Pro to your CI/CD pipeline to the AI agents your teams build with.

Nothing installed, nothing touches production. First results within hours of access to your model.
Omnext
~20 yrsspecialising in software analysis
1,000+Mendix applications scanned
1,500+automated scans every day
100+clients worldwide
The shift

Development keeps accelerating. Who is reviewing the work?

Low-code made teams fast. AI is making them faster still. Every release that ships quicker still has to be maintainable, reliable and secure.

Omnext is the independent, automated reviewer that keeps up.

Yesterday

Low-code

Mendix turns ideas into apps in days, not months.

Today

AI-assisted

AI co-develops your Mendix app, commit after commit.

Next

Agentic

Autonomous agents build and change software on their own.

One engine, every touchpoint

One engine, every touchpoint.

The same proven analysis runs wherever Mendix work happens, so quality and security are continuous, not a checkpoint at the end.

01

Portal

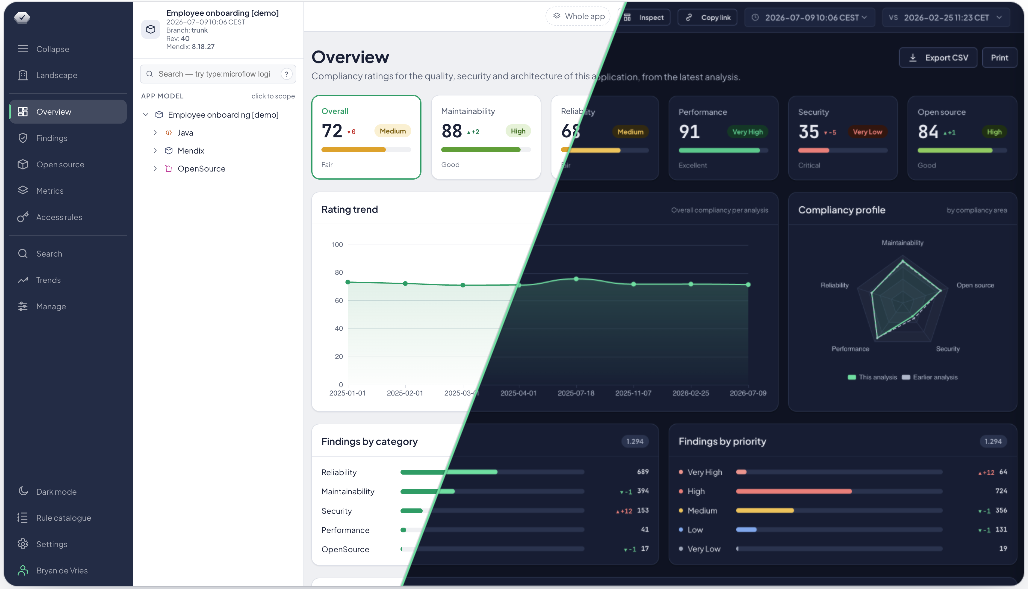
The Software Analysis Platform: dashboards, findings and rule sets for your whole Mendix landscape.

Quality + Security Analysis
02

CI/CD

Analyses run with every deployment, on every change. Quality gates that block what should not ship.

Pipeline integration (API)
03

IDE

Scan changes as you build, right inside Studio Pro. No uploads, no waiting.

DevAssist
04

AI agents

AI assistants consult Omnext's analysis in-context. Read-only, always in your control.

Omnext MCP
What you get

Two modules. One transparent score.

Use them separately or together. Both feed the Omnext Compliancy Rating: absolute, formula-based and reproducible, so your CoE controls the rulebook.

Quality Analysis · portal & pipelineOffering 01

Quality Analysis for Mendix

Build Fast. Stay in Control.

Low-code speed quietly erodes maintainability, performance and reliability. Manual reviews are slow, inconsistent and do not scale.

Configurable best-practice rule sets, ISO 25010 based
Architecture and module-dependency analysis
Custom Java code analysis
Portfolio and application dashboards with progress over time
Security Analysis · SAST for MendixOffering 02

Security Analysis for Mendix

Build Fast. Stay Secure.

Overly broad user roles, weak access rules, misconfigured microflows. The only SAST tailored to Mendix, built with The S-Unit.

The S-Unit Security Top 10 for Mendix
Access rule analysis with a full CRUDE matrix
Open source and SBOM scanning for licences and CVEs
The most critical vulnerabilities surfaced with every change
Proof & outcomes

What continuous analysis delivers.

Measured against ISO 25010 and the S-Unit Top 10. Supports continuous ISO 27001 and SOC 2 monitoring.

10–25%of developer time goes to manual peer review

Automate it and free your experts for building.

Dailyfewer production surprises

Frequent automated scans catch issues as they emerge, not after a breach or outage.

Audit-readyaccept and track findings

Accepted findings land in an audit trail. Report to stakeholders with data that is always current.

1 viewportfolio oversight

One dashboard tracks the technical health and security of your entire Mendix landscape.

Free self-assessments

Start with an honest look at your own estate.

Three short self-assessments. Answer the questions, leave your details, and your result appears on screen.

10 questions · ±4 min

Mendix Security Self-Assessment

Ten questions along the S-Unit Top 10. About four minutes. Replace "I think so" with "here is the evidence".

20 questions · ±5 min

Mendix CoE Maturity Scan

Twenty questions across governance, quality assurance, security, delivery automation and people.

Why Omnext

Purpose-built. Proven. Everywhere you build.

Built for Mendix

Designed for low-code from the ground up, not a generic tool retrofitted with indicators that do not fit.

One engine, every touchpoint

Portal, CI/CD, IDE and AI agents: the same analysis wherever your teams work.

A live ruleset

Continuously expanded with the latest insights from Mendix partners and the community.

Security depth

The only SAST tailored to Mendix, powered by The S-Unit and the S-Unit Top 10.

Automated peer review

Objective, repeatable analysis across your whole portfolio. Deterministic: the same model scores the same twice.

Transparent SaaS

A recurring subscription with unlimited scans, unlimited users, premium support and free onboarding.

FAQ

Questions we hear most

Straight answers to the questions Mendix teams ask us first.

How is Omnext different from QSM?
QSM is a portfolio tool powered by SIG with a closed industry benchmark. Omnext is the Mendix specialist: a transparent, formula-based score your CoE controls, SAST on the S-Unit Top 10, access rule analysis with a CRUDE matrix, and the same engine inside Studio Pro and your AI tooling.
What happens in the first week?
You give Omnext access to your model. Nothing is installed and nothing touches production. First results arrive within hours; onboarding, training and SSO configuration are free.
Does Omnext use AI in the analysis?
No. The analysis is deterministic static analysis of the Mendix model, its modules and dependencies. The same model scores the same twice. AI assistants can consult the results through the Omnext MCP, read-only.
Can we decide which rules count?
Yes. You toggle rules on or off and set priorities and thresholds per rule set. Omnext curates the live ruleset; your CoE owns the rulebook.
Next step

Take control of your Mendix quality and security.

A demo takes an hour of your (team's) time. Learn what our platform can, and cannot do. Your questions answered on the spot.